Loading the product…
Loading the product…
Attention: Due to high order volume, orders may require an additional business day to process.
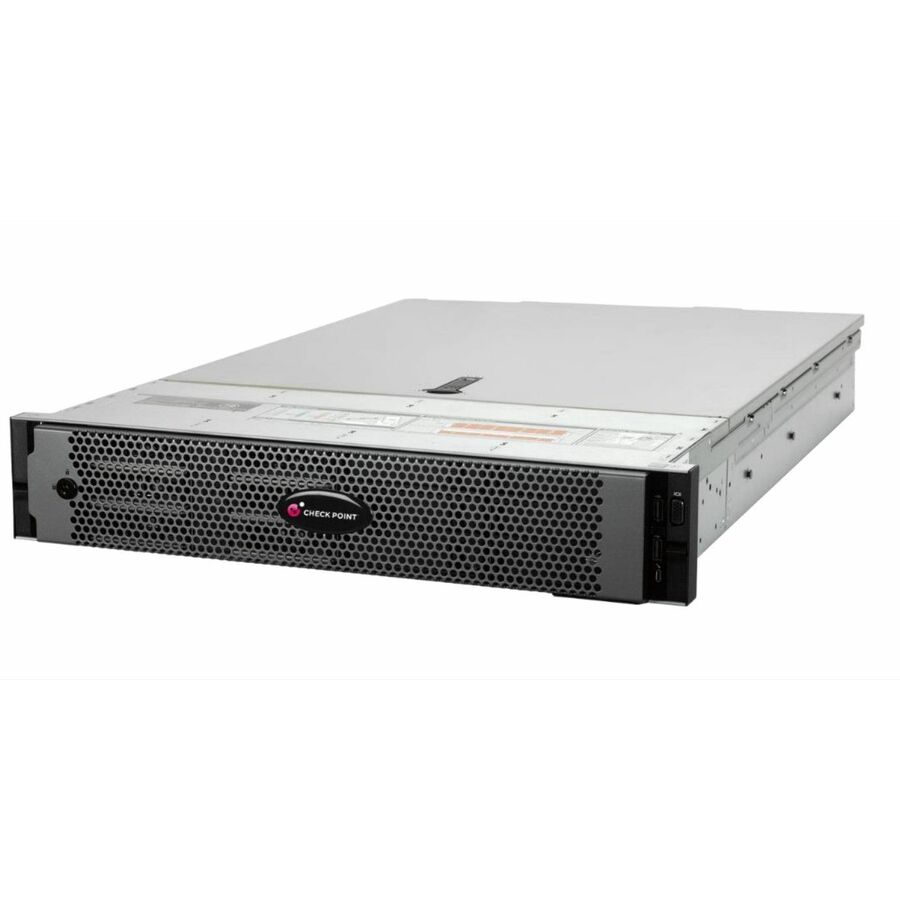
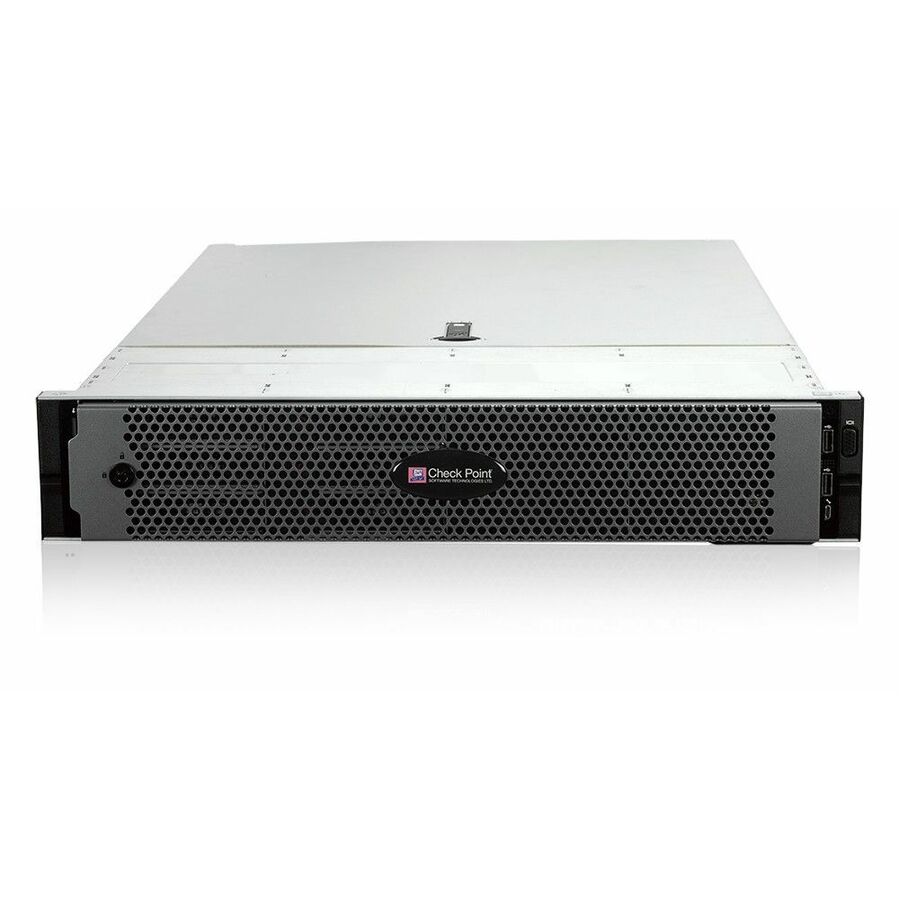
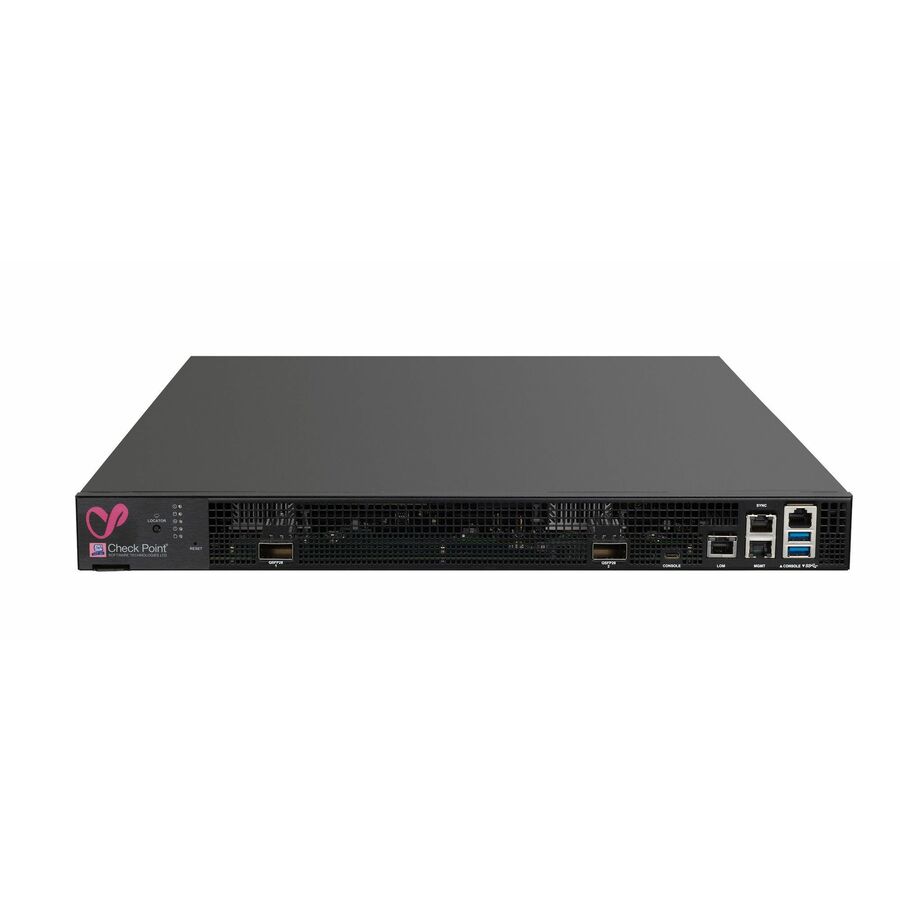
Wired - Threat Emulation - 2 Port - 10/100/1000Base-T, 100GBase-X, 10GBase-SR - 100 Gigabit Ethernet - 2 x RJ-45 - 2 Total Expansion Slots - 47 Hz, 63 Hz - 1U - Rack-mountable, Rail-mountable
MSRP$275,095.00
$255,027.28
Save 7%Special order — estimated OEM lead time 3–8 weeks. Order today and we expect to receive stock between Oct 27 and Dec 1, then process your delivery right after.
Genuine Check Point Software Technologies through authorized distribution — NDAA §889 screened before checkout. TAA verified on request.
Country of origin is manufacturer-reported and can vary by production lot. Where TAA applies to your purchase, we verify the shipping unit's origin on request.
With the increase in sophistication of cyber threats, many targeted attacks begin with exploiting software vulnerabilities in downloaded files and email attachments. New and undiscovered threats require new solutions that go beyond signatures of known threats.
SandBlast Zero-Day Protection
Check Point SandBlast Zero-Day Protection, with evasion-resistant malware detection, provides comprehensive protection from even the most dangerous attacks while ensuring quick delivery of safe content to your users. At the core of our solution are two unique capabilities-Threat Emulation (sandboxing) and Threat Extraction (Content Disarm & Reconstruction) that take threat defense to the next level.
Evasion-resistant Sandbox
As part of the Check Point SandBlast solution, the Threat Emulation engine detects malware at the exploit phase, even before hackers can apply evasion techniques attempting to bypass the sandbox. Files are quickly quarantined and inspected, running in a virtual sandbox to discover malicious behavior before it enters your network. This innovative solution combines CPU-level inspection and OS-level sandboxing to prevent infection from the most dangerous exploits, and zero-day and targeted attacks.
Content Disarm & Reconstruction (CDR)
In addition, the SandBlast Threat Extraction (CDR) capability immediately provides a safe version of potentially malicious content to users. Exploitable content, including active content and various forms of embedded objects, are extracted out of the reconstructed file to eliminate potential threats.
Access to the original suspicious version is blocked, until it can be fully analyzed by SandBlast Zero-Day Protection. Users have immediate access to content, and can be confident they are protected from the most advanced malware and zero-day threats.
SANDBLAST APPLIANCES
We offer a wide range of SandBlast Appliances. These are perfect for customers who have regulatory or privacy concerns preventing them from using the SandBlast Threat Emulation cloud-based service.
Unknown Threat Protection
The SandBlast Threat Emulation technology employs the fastest and most accurate sandboxing engine available to pre-screen files, protecting your organization from attackers before they enter your network. Traditional sandbox solutions detect malware behavior at the OS level-after the exploitation has occurred and the hacker code is running. They are therefore susceptible to evasion. SandBlast Threat Emulation capability utilizes a unique CPU-level inspection engine which monitors the instruction flow at the CPU-level to detect exploits attempting to bypass OS security controls, effectively stopping attacks before they have a chance to launch.
SandBlast Threat Extraction removes exploitable content, including active content and embedded objects, reconstructs files to eliminate potential threats, and promptly delivers sanitized content to users to maintain business flow.
Configure Threat Extraction in one of two ways: Quickly provide a reconstructed document to the user, or await response from SandBlast Threat Emulation before determining whether or not to reconstruct the document.
Inspect Encrypted Communications
? Files delivered into the organization over SSL and TLS represent a secure attack vector that bypasses many industry standard implementations. Check Point Threat Prevention looks inside these protected SSL and TLS tunnels to extract and launch files to discover hidden threats.
Limited Warranty: 1 Year
| General Information | |
|---|---|
| Manufacturer | Check Point Software Technologies, Ltd |
| Manufacturer Part Number | CPAP-SBTE2000XN-56VM |
| Brand Name | Check Point |
| Product Line | Quantum |
| Product Model | TE2000XN-56VM |
| Product Name | Quantum TE2000XN-56VM Network Security Appliance |
| Product Type | Network Security Appliance |
| I/O Expansions | |
| Total Number of Expansion Slots | 2 |
| Expansion Slot Type | QSFP28 |
| Interfaces/Ports | |
| Total Number of Ports | 2 |
| Number of Network (RJ-45) Ports | 2 |
| Network & Communication | |
| Ethernet Technology | 100 Gigabit Ethernet |
| Network Standard | 10/100/1000Base-T, 100GBase-X, 10GBase-SR |
| Physical Characteristics | |
| Compatible Rack Unit | 1U |
| Form Factor | Rack-mountable, Rail-mountable |
| Height | 1.7" |
| Width | 17.4" |
| Depth | 24" |
| Weight (Approximate) | 28.66 lb |
| Power Description | |
| Frequency | 47 Hz, 63 Hz |
| Power Consumption | 438 W |
| Technical Information | |
| Functionality | Threat Emulation |
| Firewall Protection Supported | SandBlast Threat Emulation, SandBlast Zero-Day Protection, SSL Inspection, TLS Inspection |
| Data Link Protocols | HTTP, SMTP, HTTPS, SMTPS, IMAP, FTP, SMB |
| Connectivity Technology | Wired |
| Warranty | |
| Limited Warranty | 1 Year |
| Wireless Specifications | |
| Wireless LAN | No |
| Miscellaneous | |
| Package Contents |
|
| Environmentally Friendly | Yes |
| Environmental Compliance | Restriction of Hazardous Substances (RoHS), Waste Electrical and Electronic Equipment Directive (WEEE) |
| Country of Origin | Taiwan |
Matched on Up to 5 · Rack-mountable
$2,399.25
Back-ordered$3,047.25
Back-ordered$5,571.55
Back-ordered$166,257.45
Back-ordered$162,296.16
Back-orderedSend a bill of materials or part numbers — we confirm stock and a below-market total, with TAA verified on request. No payment up front.