TAA (FAR 52.225-5) and NDAA §889 screening performed on every line before a quote is issued. Hardware sourced through US distribution.
Scope
Zero-trust segmentation · NGFW · XDR · ISE · hardening
Deliverables
Config baselines · change records · hardening evidence
Compliance
FIPS 140-2/3 options · DoDIN APL paths · §889 screened
Built for
RMF & CMMC evidence · federal and SLED programs
Overview
Zero trust has to land on a network that is already running
Zero trust is easy to draw and hard to land on a network already carrying production traffic. Most of the work is in the order of operations: read how traffic really moves, put enforcement where it concentrates, build the firewall rule base from that model rather than from the old one, then harden against the baseline your assessor is going to read. We deploy the next-gen firewalls, XDR and identity services (ISE) as one program, with FIPS 140-2/3 modules and DoDIN APL-listed hardware where the requirement calls for it.
How we work
Architecture, deployment, hardening — one program
We start from your network segmentation goals and compliance framework — RMF, CMMC, or an internal control set — and design a zero-trust architecture around policy enforcement points that actually match your traffic patterns, not a generic vendor reference diagram.
Deployment includes NGFW policy build-out, XDR sensor rollout and identity-services (ISE) integration for posture-based access control, followed by a hardening pass against CIS benchmarks or your program's STIG baseline before the system goes live.
Zero-trust segmentation mapped to your traffic and compliance framework
NGFW policy design, deployment and tuning
XDR sensor rollout and ISE-based identity and posture control
Hardening to CIS benchmarks, STIGs or program-specific baselines
Segmentation begins as a picture of how traffic actually flows — which systems talk to which, east-west between workloads and north-south to users and the outside — read from the real network rather than assumed from an org chart. Enforcement points are then placed where that traffic concentrates, and trust zones and segment boundaries are drawn around the dependencies the network really has, so a policy that looks clean on a diagram doesn't sever an application nobody wrote down.
Segmentation is translated into enforceable policy on the firewalls and NAC that gate the traffic, and the rollout is phased so an existing production network adopts it without a forklift cutover.
Segmentation model mapped to traffic flows and your control framework
Policy enforcement points sized to east-west and north-south traffic
Incremental rollout onto a live network — no disruptive cutover
Segmentation validated against the STIG or CIS baseline before go-live
NGFW work is more than racking an appliance: HA pairs, zone and interface design, and a rule base built from the segmentation model instead of migrated wholesale from a legacy firewall that nobody fully trusts anymore.
Tuning happens against real traffic — application identification, IPS and threat-prevention profiles, and decryption where policy allows — with FIPS-validated firmware confirmed before it's quoted where the requirement calls for it.
HA firewall pairs with zone and interface design
Rule base built from the segmentation model, not lifted from legacy
Application-ID, IPS and threat-prevention profile tuning
FIPS 140-2/3 validated firmware confirmed before quote where required
XDR & identity-based access (ISE)
XDR sensors are rolled out across endpoints and network taps and routed into the SIEM or analytics platform you already run — visibility that lands in your existing console, not a parallel silo your team has to watch separately.
Identity services (ISE) enforce posture- and identity-based access control: 802.1X, device profiling and posture assessment gate what reaches the network, integrated with the directory and identity provider you already operate.
XDR sensor deployment across endpoints and network taps
Telemetry routed into your existing SIEM or analytics platform
ISE 802.1X, device profiling and posture-based access control
Integration with your existing identity provider and directory
Hardening & compliance evidence
Federal and regulated buyers need more than a security posture — they need evidence. Every NGFW, sensor and identity appliance we deploy is hardened against CIS benchmarks or your program's STIG baseline before go-live, and comes with configuration baselines and change records that map back to your control framework, so an assessor reviewing RMF or CMMC evidence finds a system built to the standard, not retrofitted to explain it.
Where a requirement specifies FIPS 140-2/3 validated cryptographic modules or DoDIN APL-listed hardware, we confirm the specific model and firmware revision hold that listing before it's quoted — not after it's installed.
Hardening to CIS benchmarks, DISA STIGs or program baselines
Config baselines and change records mapped to RMF or CMMC controls
FIPS 140-2/3 validation confirmed by model and firmware revision
DoDIN APL listing paths verified before hardware is quoted
NDAA §889 screening on every line
What's included
From architecture to hardened, evidenced deployment
Zero-trust network segmentation design and policy enforcement mapping
NGFW deployment, policy build-out and tuning
XDR sensor deployment across endpoints and network taps
ISE integration for identity- and posture-based access control
Hardening to CIS benchmarks, DISA STIGs or program baselines
FIPS 140-2/3 and DoDIN APL hardware verification where required
Fielded hardware
Platforms we field in this lane
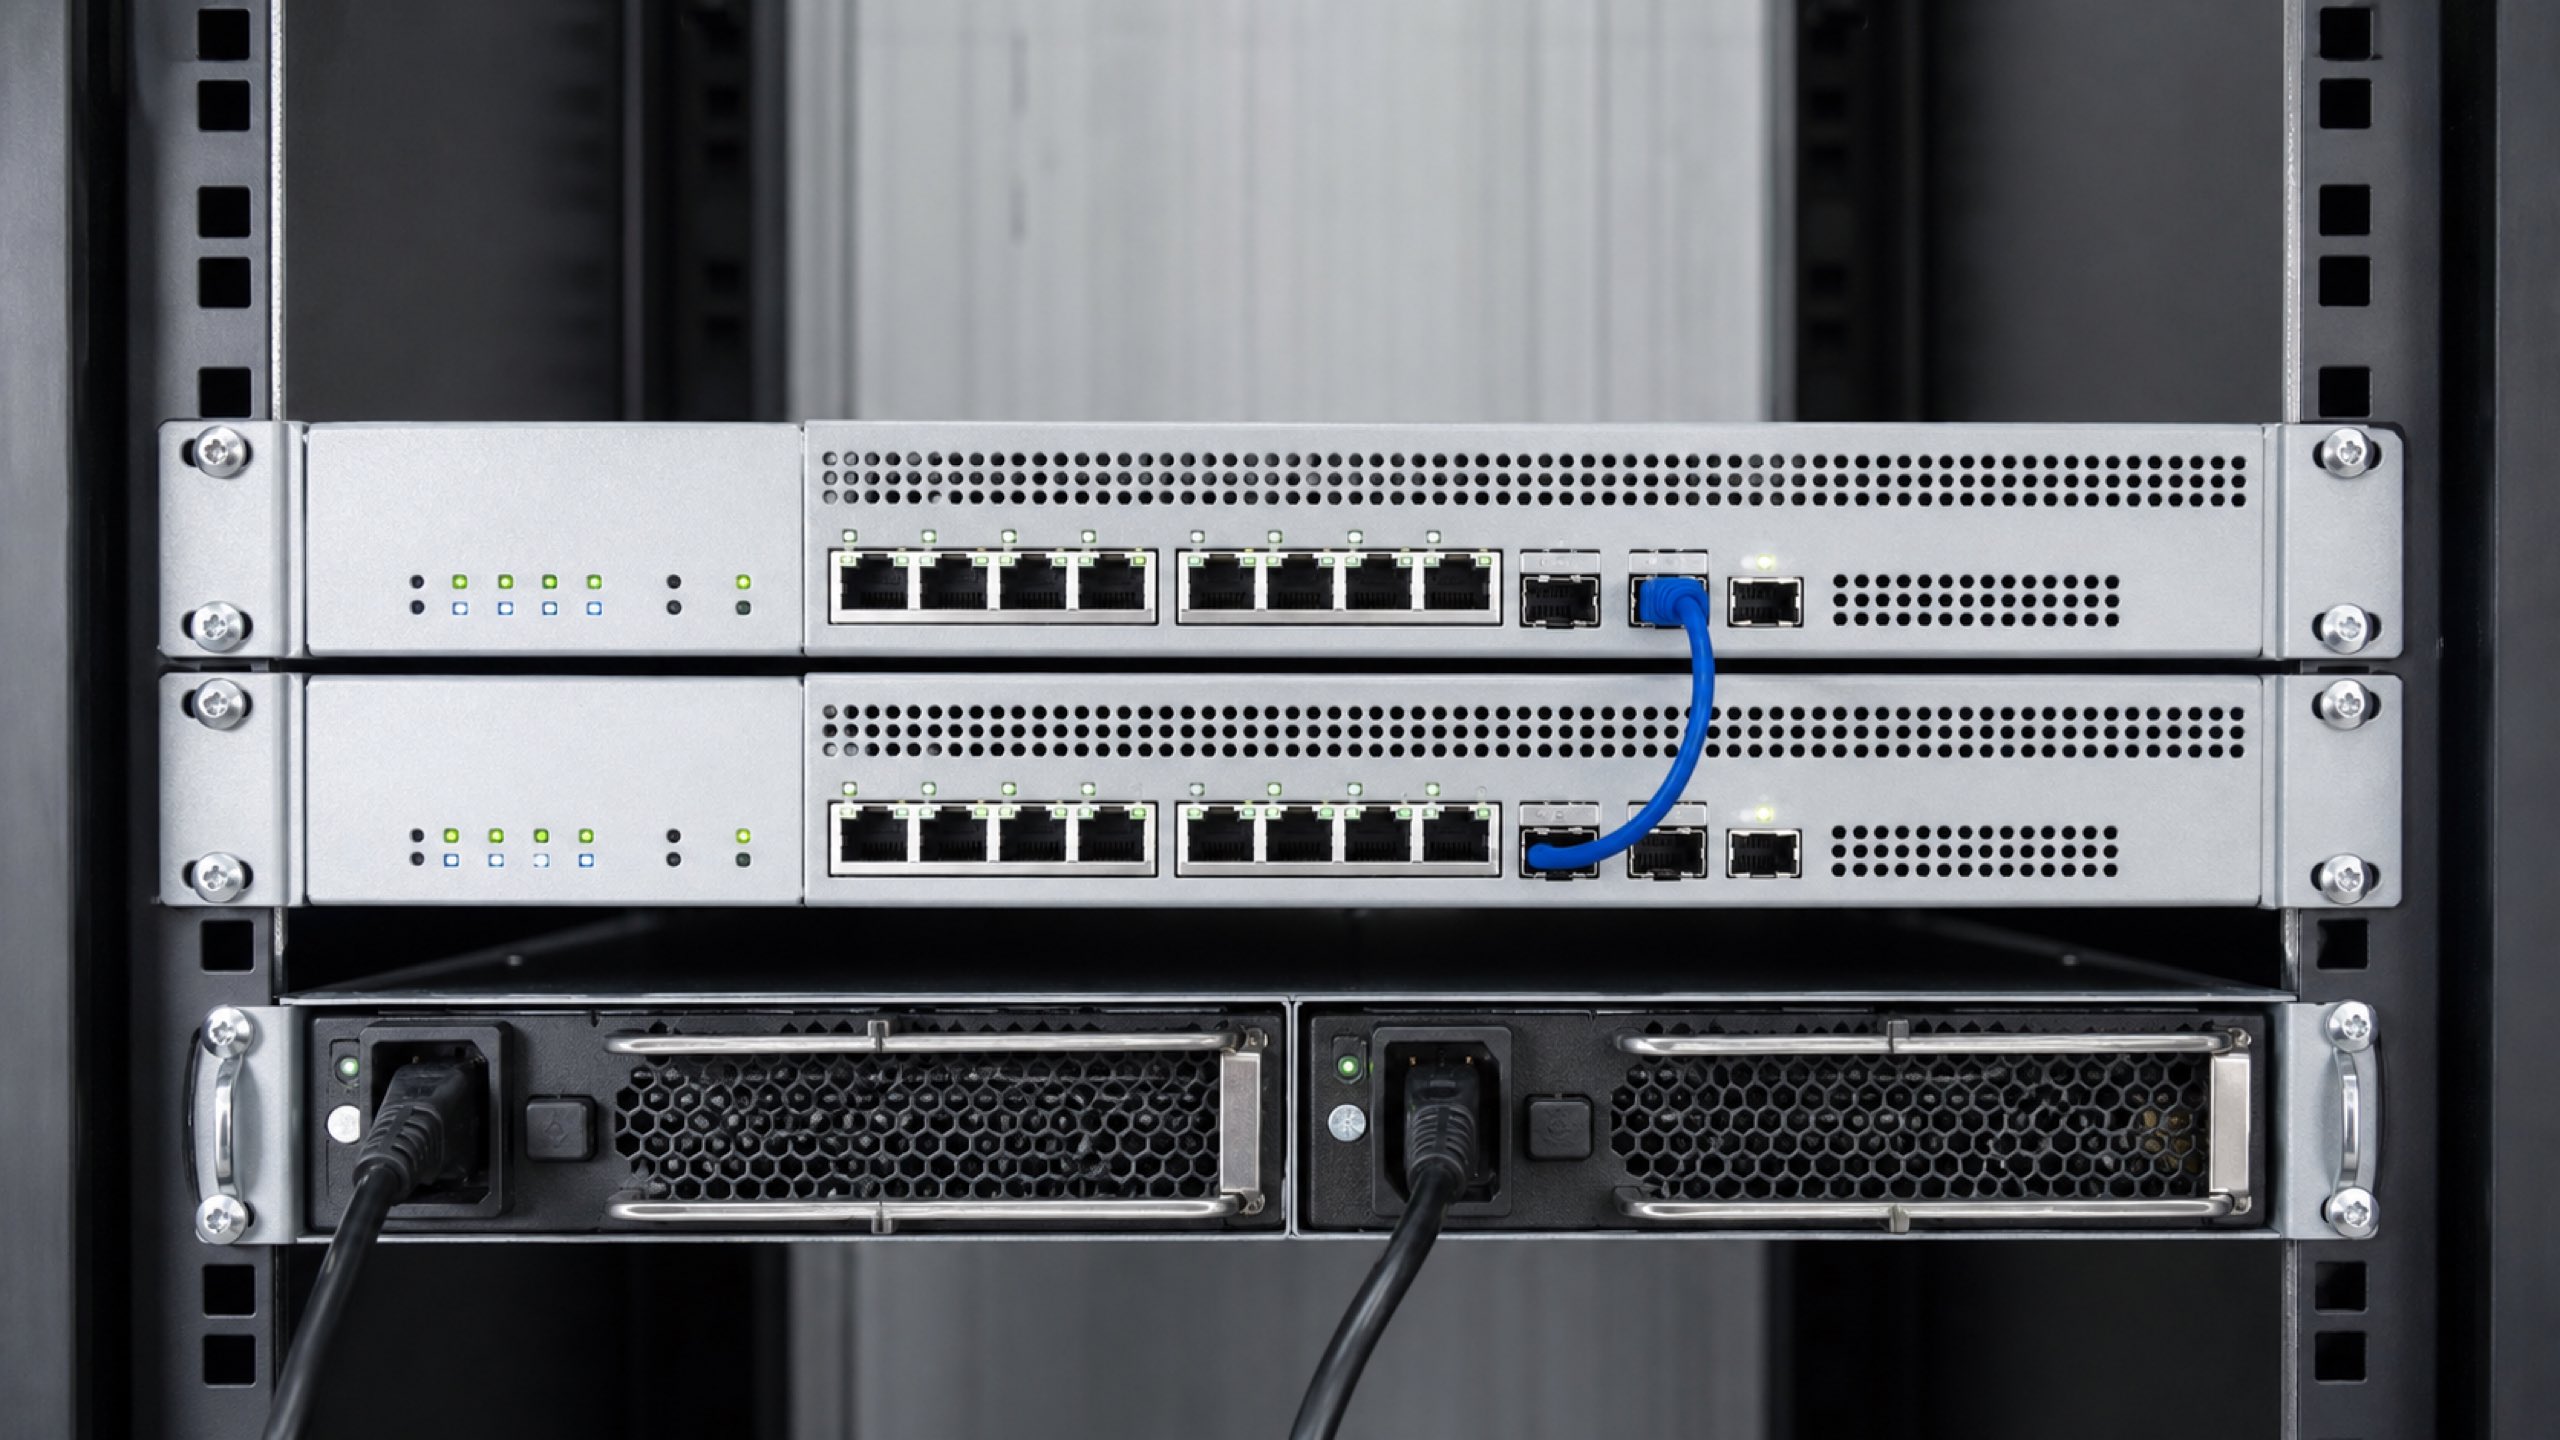
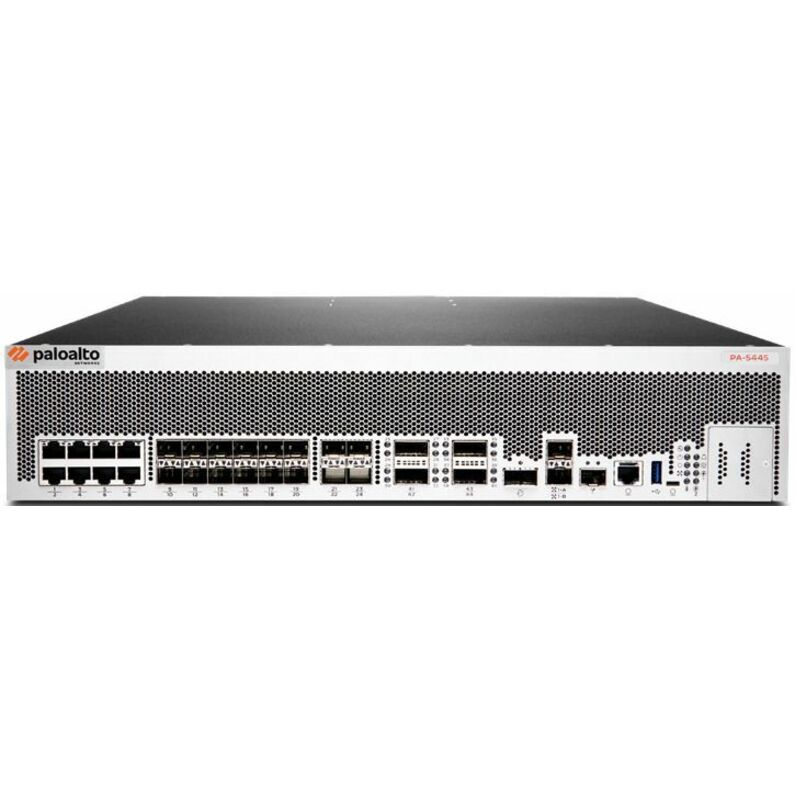
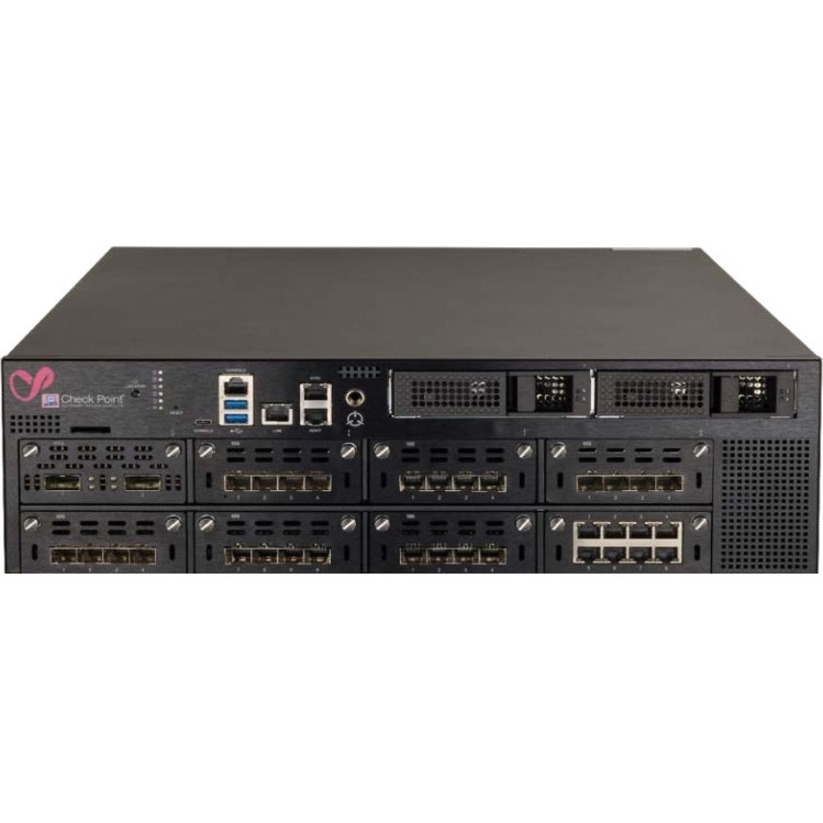
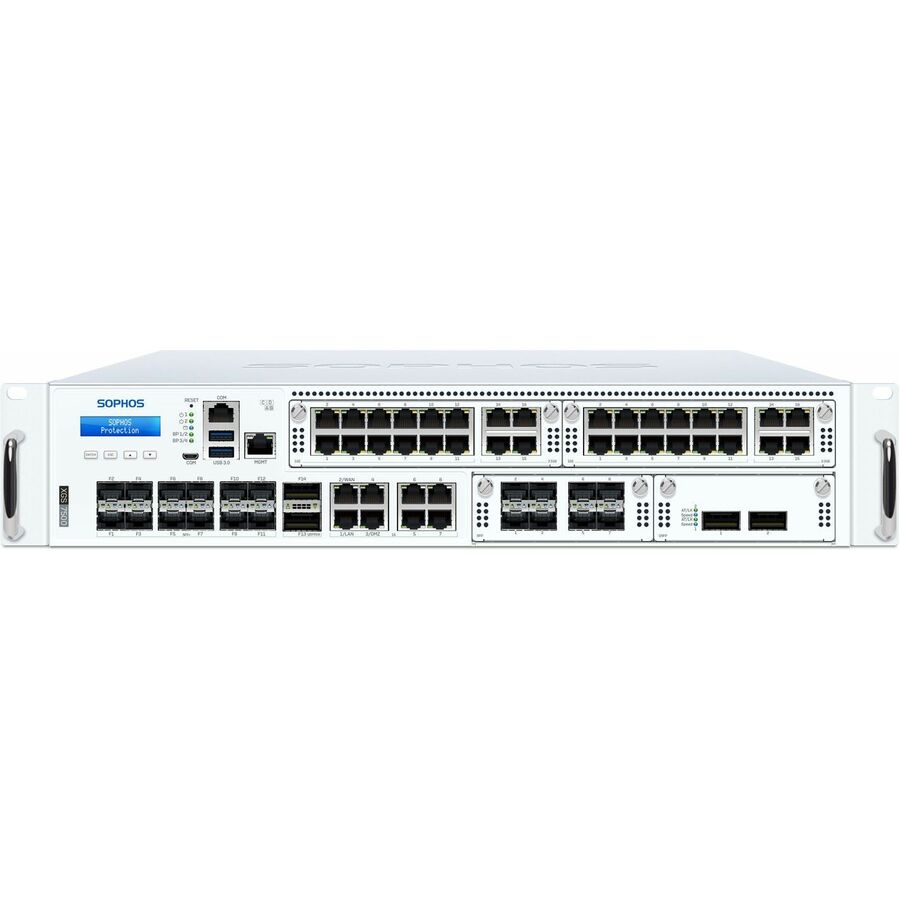
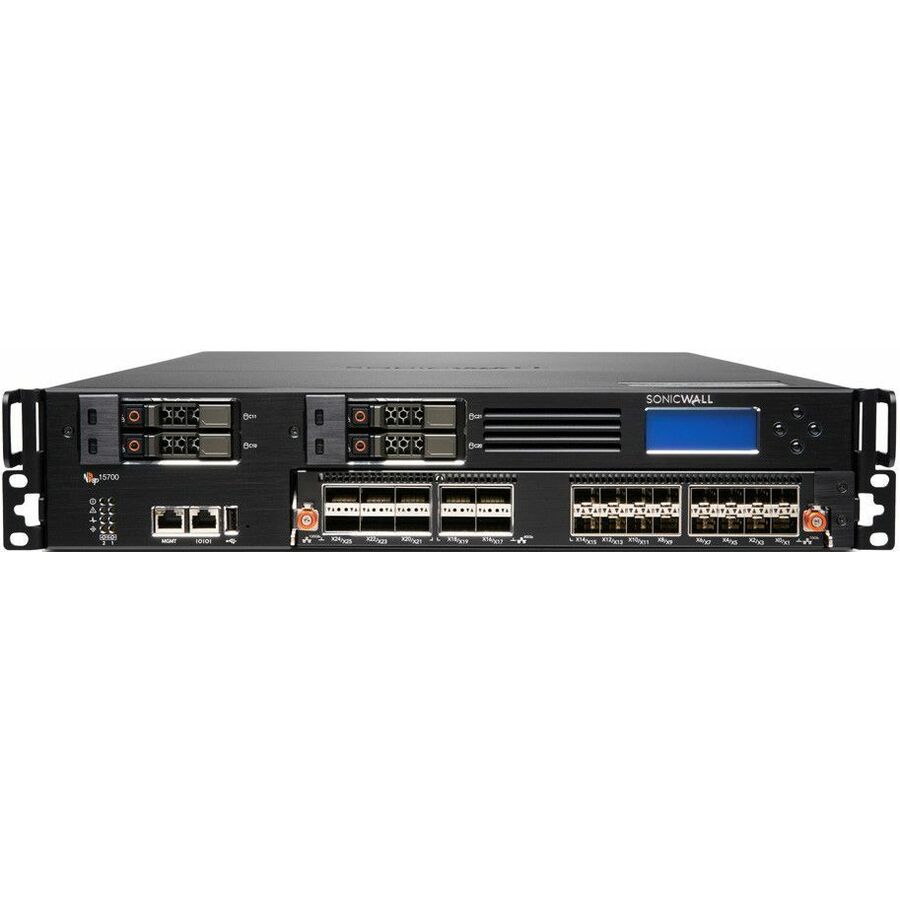
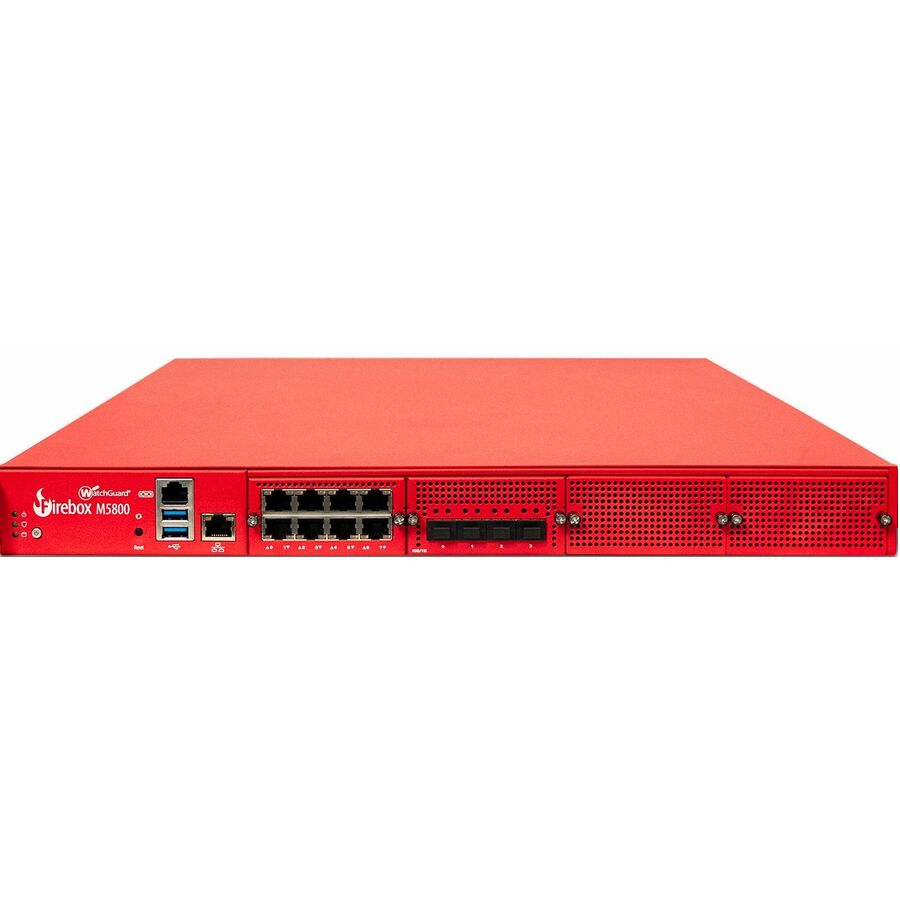
Representative hardware from the live Uniqcli catalog: sourced through US distribution, screened line by line, and configured for the program before it ships.
The configuration baselines, hardening evidence and change records this lane produces are what a CMMC Level 2 or RMF assessor reads. These pages map the NIST SP 800-171 families onto what is actually quotable behind them.
Can you deploy into an existing network without a full redesign?
Yes. Most engagements layer zero-trust segmentation, NGFW policy and XDR visibility onto an existing network incrementally, phased to avoid a disruptive cutover.
Do you support CMMC or RMF assessment evidence?
Yes. Configuration baselines, change records and hardening documentation are captured during deployment and organized to map to your control framework for assessor review.
Can you supply FIPS-validated or DoDIN APL-listed hardware specifically?
Yes. We confirm the exact model and firmware revision carry the required FIPS 140-2/3 validation or DoDIN APL listing before quoting, and document it with the order.
Do you provide 24/7 monitoring, a SOC or an incident-response retainer?
No. Uniqcli deploys, integrates and hardens security products — firewalls, XDR sensors, identity services — and hands off a tuned, documented system to your security-operations team or the MDR provider you've chosen. We are not a managed SOC, MDR or incident-response provider; the ongoing watch stays with your team.
Can XDR and identity services feed our existing SIEM and identity provider?
Yes. XDR telemetry is routed into the SIEM or analytics platform you already run rather than a parallel console, and ISE integrates with your existing directory and identity provider, so posture-based access builds on the identities you already manage instead of a new silo.
How an engagement runs
From requirement to delivered, in four steps
1
Brief
Send the requirement as it exists: a statement of work, drawings, a bill of materials or a problem statement. A briefing call scopes it against the lines above.
2
Scope and quote
Feasibility, country-of-origin and §889 screening, and lead times come back with a line-item quote. Nothing is committed until the scope is agreed.
3
Build and integrate
Manufacture, rack, image, configure and test in the facility, so the first time the system is assembled is not on install day.
4
Deliver and sustain
Delivery with serialized chain-of-custody records, then warranty, RMA and lifecycle support on the same relationship.
Compliance and documentation
Screened before it is quoted, documented when it ships
Country of origin and §889 status are checked per line while the quote is being built, not after a program review asks. The same record travels with the order: what was sourced, where it came from, who handled it and when it shipped.
TAA (FAR 52.225-5) country-of-origin screening on every line
NDAA §889 covered-equipment screening on every line
FIPS 140-2/3 validated options where the requirement calls for it
DoDIN APL listing paths verified before a quote is issued
Section 508 / VPAT documentation available on request
Serialized chain-of-custody records delivered with every shipment
A network diagram, or the control framework you answer to, is where this begins. Back comes an architecture, a phased deployment plan and the hardware quote behind it.