CMMC vs FedRAMP vs NIST 800-171: Which Evidence Applies
CMMC is a Department of Defense contracting and assessment program. NIST SP 800-171 is a set of security requirements for protecting CUI in nonfederal systems. FedRAMP is a government-wide assessment and certification program for cloud services used by federal agencies. They can overlap in one architecture, but none is a universal substitute for the others.
Section 889 Surveillance BOM: A Component-Level Checklist
Section 889 compliance screening cannot stop at the logo on a camera. A defensible review follows the system through cameras, recorders, radios, management software, cloud services, and the entities that provide them—then preserves the manufacturer and supplier evidence behind the decision.
CMMC Phase II Is Suspended: What Contractors Still Owe
CMMC Phase 2 (Phase II) was suspended on July 13, 2026, but the Department did not suspend the cybersecurity clauses already in contracts, Phase I self-assessments, SPRS reporting, or the obligation to give the government accurate representations. Treat the pause as time to improve evidence and scope—not permission to stop.
CMMC Hardware Requirements: What the Controls Really Require
CMMC compliance does not begin with a product certificate or universal hardware list. CMMC assesses how an organization protects information within a defined system boundary. Hardware matters when it implements a requirement—such as segmentation, multifactor authentication, encryption, logging, recovery, or physical protection—but the evidence must show the exact device is configured, operated, and maintained as part of the system.
CMMC MFA: Where Hardware Security Keys Fit
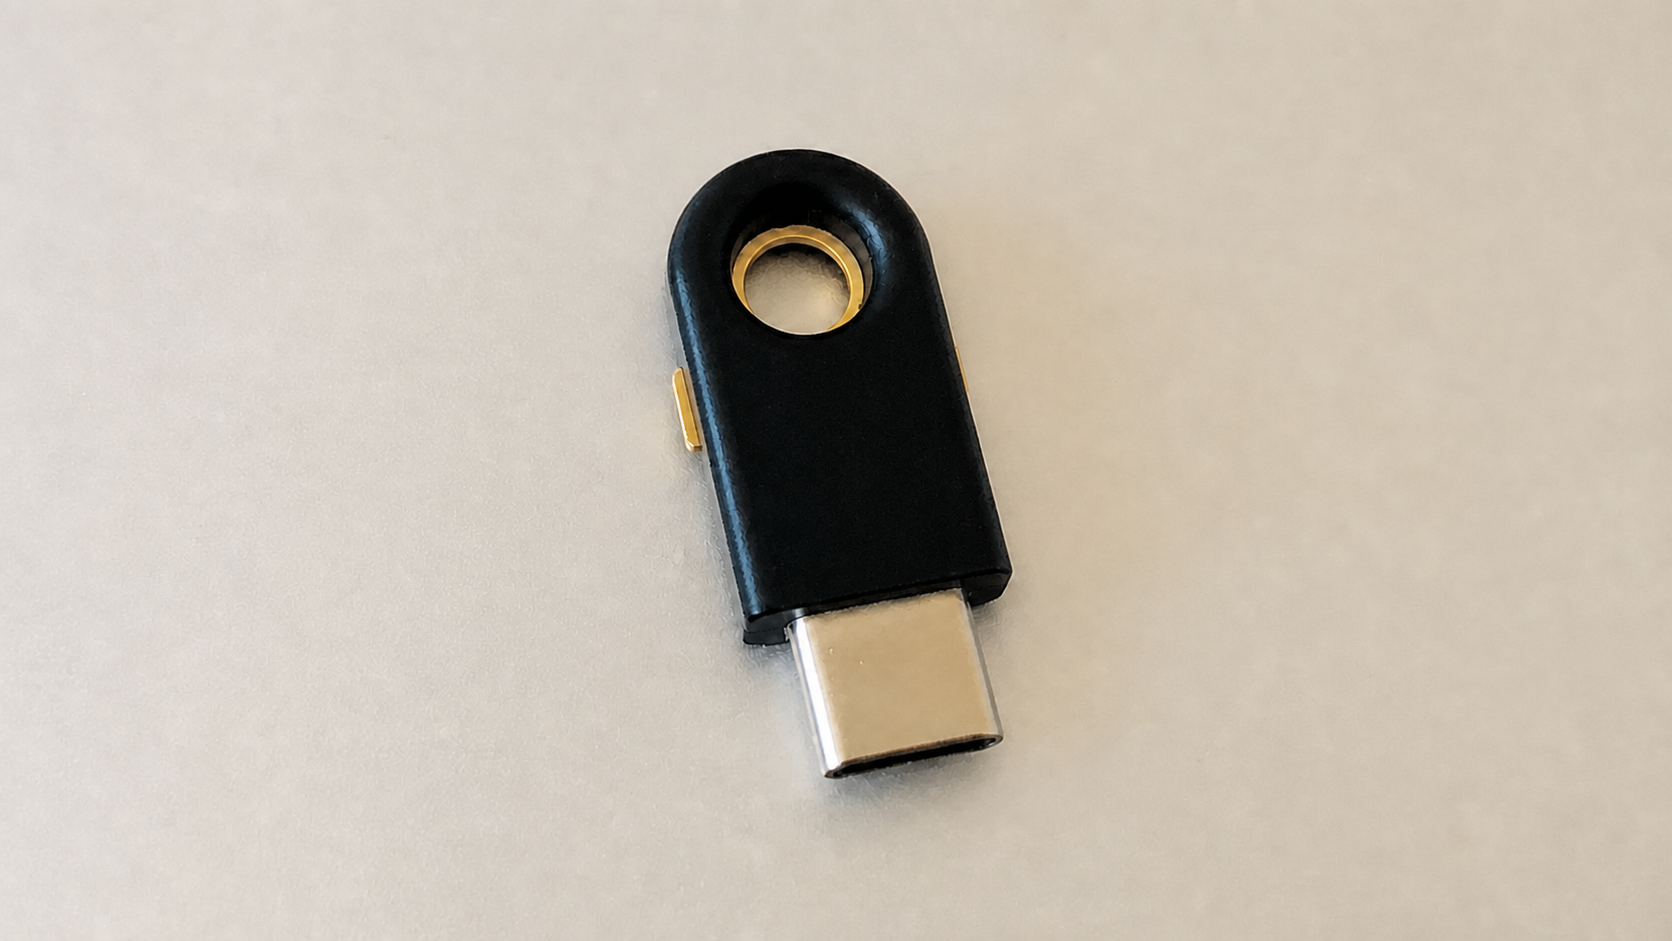
A FIPS security key is not a standalone CMMC requirement, and CMMC does not mandate one authenticator brand. At Level 2, the current NIST SP 800-171 Revision 2 baseline requires MFA for local and network access to privileged accounts and for network access to non-privileged accounts, plus replay-resistant authentication for network access. PIV, CAC, FIDO2, and other cryptographic authenticators can fit—but only when the complete identity system, fallback path, enrollment, recovery, and evidence meet the requirement.
Section 889 in 2026: The Loophole Just Closed and the List Keeps Growing
The FCC's June 2026 vote didn't create new restrictions — it deleted the loophole that let integrators keep selling legacy Hikvision and Dahua stock. Here is what actually changed, and why a SAM.gov checkbox no longer covers you.
NIST 800-171 Checklist for Hardware Buyers
Most NIST 800-171 gap assessments come back with findings that trace to a switch, a server, or an endpoint — not a policy document. Here is what to check before the assessor does.
CJIS Security Policy Network Requirements Checklist
Dispatch centers and records units pass CJIS audits on paperwork more often than on the network itself — here's where the technical controls actually live.
Cyber Insurance Requirements: What Insurers Now Demand Before They Write a Policy
Underwriters stopped taking IT security posture on faith. Here is what the questionnaire actually checks, and the hardware and software that gets an organization to "yes."
FedRAMP 20x: What Changes in a Cloud Evidence Package
FedRAMP 20x moves cloud-security evidence toward machine-readable rules, persistent validation, Security Decision Records, and Key Security Indicators. It does not remove an agency’s responsibility to define its use case, assess customer-controlled components, authorize the complete agency system, or verify that the purchased service and integrations match the certified offering.
HIPAA Security Rule Network Requirements: What Your Infrastructure Must Do
The Security Rule's technical safeguards do not stop at your EHR. Access control, audit controls, and transmission security reach into the switches, firewalls, and wireless that carry protected health information.
FIPS 140-2 Goes Historical: What New Purchases Need
FIPS 140-2 modules remain acceptable for new federal systems through September 21, 2026. On September 22, the remaining certificates move to the CMVP Historical List. That is not a recall: NIST says agencies may continue using those modules in existing systems, while new-system purchases should move to modules with active FIPS 140-3 validations.
CMMC in 2026: The Mandate Is Live, But the Queue Is the Problem
The 48 CFR rule armed DoD's award-blocking authority in November 2025. Halfway through 2026, the binding constraint for most contractors isn't passing an assessment — it's getting one scheduled.
What "TAA Compliant" Actually Means (and What to Demand)
TAA is not a checkbox — it's a three-layer test of threshold, country, and substantial transformation. Here's what the government now audits, and the documentation buyers should demand.
Free Guide · Compliance
TAA Compliance Checklist for Federal IT Buyers
A practical, line-by-line checklist for confirming Trade Agreements Act compliance before hardware ever reaches a contracting officer's desk.